Tag: Email

  • The Hotel Message Knows Your Real Booking. It Can Still Be a Scam.

    VERDICT: STRONGLY VERIFIED (V4)

    A scam message can know where you are staying, when you are travelling and which property you booked.

    CLAIM

    Reservation-hijack scams use genuine booking context to send travellers convincing payment or card-verification requests through channels they already associate with their trip.

    EVIDENCE

    Gen Threat Labs reported in May 2026 that it had identified more than 350 accommodation-specific reservation-hijack scam flows across 50 countries. Its dataset included 31 compromised accommodations linked to the United Kingdom. Researchers analysed fraudulent landing pages, URLs, messages and in-app evidence and said victims had received reservation-specific information before being pushed to pages customised around the accommodation.

    Gen uses “compromised accommodation” carefully: it means reservation context associated with that accommodation was compromised and used in an intercepted attack flow. The source of the compromise could vary, including accommodation accounts, partner accounts, email, property-management systems or third-party services.

    TEST

    This evidence establishes the attack model and UK presence, but it does not prove that Booking.com itself was the source of every data compromise or that all attacks used the same malware chain. TVD therefore does not make either claim.

    VERDICT

    V4 — Strongly Verified. The mechanism is strongly supported by detailed threat research with UK cases in the dataset; attribution of individual compromise points varies.

    How to prevent it

    • Do not treat correct booking information as proof that a payment request is genuine.
    • If asked to re-enter card details or make an unexpected payment, open the booking service independently rather than following the supplied link.
    • Contact the accommodation using independently verified details if anything has changed.
    • If you entered card details into a suspicious page, contact your card issuer promptly.

    Warning signs

    • A message knows genuine booking details but unexpectedly asks you to re-enter payment information.
    • You are told the reservation will be cancelled unless you make another payment or verification payment.
    • The link opens a payment page outside the route you normally use to manage the booking.

    What to do if you responded

    Contact your payment provider promptly if you entered payment details or made a payment. Open the booking platform independently, check the reservation and contact the accommodation through independently verified details. Preserve the message and URL.

    Where to report it

    Report the message to the booking platform or accommodation through its genuine channels and report financial loss through the appropriate official fraud-reporting route. See Fraud First Aid.

    Source: Gen Threat Labs, “When Hotel Scams Know Your Booking”, 28 May 2026, plus its March 2026 Reservation Hijack investigation.

    Evidence boundary: TVD does not attribute all reservation-hijack attacks to any single booking platform, accommodation provider or software company.
  • The Digital Landline Switchover Is Real. The Upgrade Fee Is Not.

    VERDICT: STRONGLY VERIFIED (V4)

    The digital landline switchover is genuine. An unexpected demand that you pay to make the switch is not.

    CLAIM

    Scammers are exploiting the UK’s move from analogue landlines to digital services by posing as telecoms representatives and demanding payment or financial details.

    EVIDENCE

    UK government guidance confirms that the technology underpinning the analogue Public Switched Telephone Network is being retired by January 2027.

    Citizens Advice warns that if someone says you need to pay to switch your phone line, it is a scam and says home-phone providers will not ask customers to pay to switch to a digital phone line.

    Bromsgrove District Council warns of criminals posing as BT staff, asking for personal and payment details for an upgrade and threatening to cut off the landline if the resident refuses. Stoke-on-Trent City Council separately warns of callers requesting payment or bank details to renew telecare services.

    TEST

    The scam pretext is documented by consumer and local-government sources. TVD has not identified a national loss total for this specific method and does not claim one.

    VERDICT

    V4 — Strongly Verified.

    How to prevent it

    • Do not pay an unexpected caller for the landline switchover.
    • Contact your provider independently using details from your bill or official website.
    • If you use a personal alarm or telecare device, tell your telecoms and telecare providers so compatibility can be checked.
    • Do not let a threat of immediate disconnection rush you into giving bank details.

    Warning signs

    • An unexpected caller says you must pay for the digital landline switchover.
    • You are threatened with immediate disconnection unless you provide bank details.
    • A caller claims to represent your telecoms or telecare provider but asks you to use unfamiliar payment details.

    What to do if you responded

    Contact your telecoms provider independently using the number on your bill or its official website. If you supplied payment details, contact your bank. If you use telecare or a personal alarm, separately confirm compatibility with the genuine provider.

    Where to report it

    Report the approach to the genuine provider and use the appropriate official fraud-reporting route if money or sensitive information was taken. See Fraud First Aid.

    Sources: GOV.UK digital-landline guidance; Citizens Advice; Bromsgrove District Council; Stoke-on-Trent City Council.

  • The Trademark Email That Says Someone Else Is About to Take Your Business Name

    VERDICT: VERIFIED (V5)

    The message sounds like professional legal correspondence: somebody else is supposedly about to register your business or brand name, but you have one last chance to act first.

    CLAIM

    Businesses are receiving trademark approaches that misuse the identities or regulatory details of genuine solicitors and firms.

    EVIDENCE

    The Solicitors Regulation Authority (SRA) has issued repeated alerts during 2026 describing closely similar approaches. The emails tell recipients that a third party has approached the sender to register the recipient’s UK brand or company name and seek exclusive rights. The recipient is then invited to secure trademark registration first, with the sender offering assistance.

    SRA alerts dated 8 April, 7 May, 13 May, 16 June, 13 July, 16 July, 19 August, 9 September and 10 September 2026 document variants misusing names or details associated with genuine solicitors or firms.

    TEST

    The repetition across separate SRA alerts establishes the recurring method. It does not establish that every approach came from one criminal group, and TVD makes no such attribution.

    VERDICT

    V5 — Verified.

    How to prevent it

    • Do not treat an SRA number or a genuine solicitor’s name as proof that the sender is that person.
    • Look up the solicitor or firm independently using the SRA’s official records and use independently obtained contact details.
    • Do not use the telephone number, email address or website supplied in the unexpected message to perform that verification.
    • If a trademark issue may be genuine, verify it independently before paying or instructing anyone.

    Warning signs

    • An unsolicited legal-looking email says somebody else is about to register your business or brand name.
    • You are pressured to instruct the sender immediately to protect the name.
    • The sender uses genuine-looking solicitor or SRA details but contact information does not match independently verified records.

    What to do if you responded

    Stop further payment or correspondence until the sender has been independently verified. If you paid, contact your bank. If you supplied account credentials, secure them. Preserve the original email, headers, attachments and payment instructions.

    Where to report it

    Check and report suspected solicitor impersonation through the SRA’s official channels and use the appropriate fraud-reporting route if money was lost. See Fraud First Aid.

    Sources: Solicitors Regulation Authority scam alerts published throughout April–September 2026.

    Evidence boundary: genuine solicitors and firms named in SRA alerts are victims of identity/detail misuse; TVD does not suggest they participated in the scam.

  • Scammed Once? The Next Caller May Pretend the FCA Has Recovered Your Money

    VERDICT: VERIFIED (V5)

    Losing money to fraud can create another vulnerability: somebody offering to get it back.

    CLAIM

    Fraudsters are impersonating the Financial Conduct Authority and telling previous fraud victims that money has been recovered, before trying to take further money or sensitive banking information.

    EVIDENCE

    The FCA said it received 4,465 reports of fake-FCA scams during the first six months of 2025. It recorded 480 people who had been duped into sending money. Almost two-thirds of reports came from people aged 56 or over.

    The regulator identified a common method in which fraudsters claimed the FCA had recovered funds from a cryptocurrency wallet opened illegally in the consumer’s name. It also identified approaches to previous loan-scam victims claiming the FCA could recover their losses, followed by attempts to obtain further funds. A separate reported variant falsely claimed that creditors had obtained a County Court Judgment and that money was owed to the FCA.

    TEST

    The figures come directly from the FCA. They cover fake-FCA scams generally, not only the recovered-money variant. TVD therefore does not attribute all 4,465 reports or all 480 payments to recovery fraud.

    VERDICT

    V5 — Verified.

    How to prevent it

    • Do not send money because an unexpected caller says the FCA has recovered previous losses.
    • The FCA says it will never ask you to transfer money to it or provide bank PINs or passwords.
    • End the contact and reach the FCA independently through its official contact details.
    • If you have previously been defrauded, be particularly cautious of unsolicited recovery offers.

    Warning signs

    • An unexpected caller says the FCA has recovered money for you.
    • You are asked to pay a fee, tax or release payment before receiving recovered funds.
    • The contact asks for PINs, passwords or a transfer of money.

    What to do if you responded

    Stop contact, contact your bank immediately if you paid or disclosed banking information, and independently contact the FCA using its official details. Preserve the telephone number, emails, payment details and any names used.

    Where to report it

    Report FCA impersonation to the FCA and report any fraud through the appropriate official fraud-reporting route. See Fraud First Aid for urgent steps after a payment or disclosure.

    Source: Financial Conduct Authority, “Almost 5,000 fake FCA scams reported in first 6 months of 2025”, 27 August 2025.

  • Your Pension Provider May Be Talking to a Fraudster Who Is Pretending to Be You

    VERDICT: VERIFIED (V5)

    Some pension fraud no longer depends on persuading the saver to make a transfer. The attacker may instead try to convince the pension scheme that they are the saver.

    CLAIM

    Fraudsters are using hacking and impersonation techniques to gain unauthorised access to pension accounts and attempt to bypass scheme security.

    EVIDENCE

    The Pensions Regulator (TPR) published an industry alert after an analyst seconded to the National Fraud Intelligence Bureau examined Action Fraud reports received between October 2024 and March 2025. TPR said almost a third of the reports analysed referenced attempts to bypass pension-scheme defences and exploit security vulnerabilities to gain unauthorised access to members’ accounts.

    Methods identified by TPR included hacking a member’s email to obtain correspondence with the pension scheme, then impersonating the member and attempting to change beneficiary bank details. TPR also identified attempts involving fake pension accounts, poorly secured credentials and diversion of deceased members’ pension funds. Members aged 50–69 represented 55% of reported victims in the analysis.

    TEST

    The finding comes from the pensions regulator and is based on analysed fraud reports. The “almost a third” figure applies to the reports in that specific October 2024–March 2025 analysis; it must not be presented as one third of all UK pension fraud.

    VERDICT

    V5 — Verified. The impersonation/account-takeover technique is directly documented by TPR.

    How to prevent it

    • Turn on two-step verification for your email and pension accounts where available.
    • Use a unique password for the email account connected to your pension.
    • Check that your pension provider holds your correct contact details.
    • Treat unexpected notifications of changed bank or contact details as urgent and contact the scheme through a known route.

    Warning signs

    • An unexpected pension notification says your bank, beneficiary or contact details have changed.
    • You receive password-reset or login alerts you did not initiate.
    • Pension correspondence disappears from or appears unexpectedly in a compromised email account.

    What to do if you responded

    Contact the pension scheme using independently verified details, ask whether any account, beneficiary or payment instructions have changed, secure the linked email account and change reused passwords. Preserve security alerts and correspondence.

    Where to report it

    Tell the pension provider immediately. If fraud or attempted fraud is identified, use the appropriate official fraud-reporting route. See Fraud First Aid if money or account access may already be affected.

    Source: The Pensions Regulator, “Industry alert: impersonation fraud”, published September 2025 and updated January 2026.

    Evidence boundary: the regulator establishes the technique and the characteristics of the analysed reports. TVD is not attributing failures to any particular pension provider.

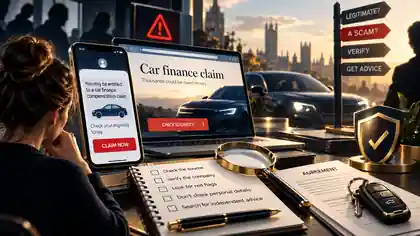
  • Car-Finance Claim Messages: Verify Before You Respond

    Car-Finance Claim Messages: Verify Before You Respond

    A message about a car-finance claim can look plausible, timely and professional. None of those things proves who sent it.

    On 22 September 2026, the Financial Conduct Authority added www.approvedcarclaim.com and www.pcp.ashley-howard.co.uk / www.ppi.ashley-howard.co.uk to its Warning List. In each warning the FCA states that the firm is not authorised by it and may be targeting people in the UK.

    The important consumer lesson is broader than any one website: when a subject is already receiving widespread public attention, a message that appears topical can feel credible before its identity has actually been checked.

    CLAIM

    If a message correctly refers to car-finance compensation or PCP claims, the sender is probably a legitimate claims or financial-services business.

    EVIDENCE

    The FCA’s Warning List shows that unauthorised firms can operate in the same subject areas consumers are actively searching for. The regulator also warns that firms may provide contact details belonging to another business or individual so that an approach appears genuine.

    TEST

    Before clicking, replying or providing personal details, separate the subject of the message from the identity of the sender.

    1. Do not use the link in the message to verify the sender. Search independently.
    2. Check the exact legal or trading name. Similar names are not the same identity.
    3. Use the FCA Firm Checker where regulated activity is involved. Compare the contact details shown there with the ones used to approach you.
    4. Do not assume an existing car-finance relationship authenticates a new claims company.
    5. Be cautious with requests for identity documents, bank details, fees or authority to act. Establish who you are dealing with first.

    VERDICT: V1 VERIFIED

    The FCA added car-finance and PCP-related websites to its Warning List on 22 September 2026. That is verified primary-source evidence that consumers should independently check the identity and regulatory status of businesses approaching them about this subject.

    It does not follow that every unsolicited car-finance claim message is fraudulent. The correct response is verification, not assumption.

    ACTION

    If you receive a car-finance compensation message, preserve it before deleting anything. Record the sender, telephone number, email address, website and any company or FCA reference numbers supplied. Then verify those details independently.

    If the approach involves a firm on the FCA Warning List, follow the FCA’s guidance and avoid dealing with it.

    Primary sources: FCA Warning List; FCA warning: www.approvedcarclaim.com; FCA warning: www.pcp.ashley-howard.co.uk / www.ppi.ashley-howard.co.uk.


    The Verification Desk distinguishes verified fact, evidence-led inference and unresolved uncertainty. Mention of a website or firm reflects the cited FCA warning and is not an independent finding of criminal conduct. This publication provides general information, not legal or financial advice.

  • The Bank-Detail Change Verification Test

    The Bank-Detail Change Verification Test

    A request to change supplier bank details may be genuine. The email containing it proves almost nothing.

    CLAIM

    A bank-detail change should be treated as a change to a control, not an ordinary administrative instruction.

    EVIDENCE

    Compromised email accounts and convincing impersonation can place a fraudulent instruction inside a genuine conversation. Familiar wording, a correct signature block and knowledge of an invoice do not establish that the payment destination is legitimate.

    TEST

    The decisive test is independent confirmation through a channel already trusted before the change request arrived.

    VERDICT

    No independent confirmation, no change. Urgency is a reason to slow the process down, not bypass it.

    ACTION: THE BANK-DETAIL CHANGE TEST

    1. Freeze the change. Do not amend the supplier record or release payment.
    2. Use a pre-existing contact. Call a known contact using a number from the existing contract, verified supplier master record or official website, not the message requesting the change.
    3. Ask open questions. Confirm the change, effective date, reason and account name without reading every detail from the request.
    4. Require dual approval. One person verifies; another approves the amendment.
    5. Record the verification. Date, time, person contacted, number used, questions asked and outcome.
    6. Notify the known contact. Send confirmation to the previously established address as well as any new address.
    7. Control the first payment. For material changes, consider an independently approved test payment or enhanced review under the organisation’s policy.

    RED FLAGS

    • Pressure to act before a deadline
    • A request to avoid the usual contact
    • A new domain, subtle spelling variation or reply-to address
    • An explanation involving an audit, frozen account or confidential transaction
    • A simultaneous change to contact and bank details
    • Resistance to established verification controls

    IF PAYMENT HAS ALREADY BEEN MADE

    Contact the bank immediately through a trusted channel. Preserve the request, full email headers, invoice, payment approval, supplier record and every verification attempt. Contact the genuine supplier using established details.

    CONTROL TEMPLATE

    Change requested: ______
    Existing trusted contact: ______
    Independent number/source: ______
    Confirmed by: ______
    Verified by: ______
    Approved by: ______
    Date/time: ______
    First-payment control: ______

    Evidence & official sources


    The Verification Desk distinguishes verified fact, evidence-led inference and unresolved uncertainty. This publication provides general information, not legal, financial, regulatory or emergency advice. Findings reflect the evidence available at publication and may be updated if material evidence changes.